Security Research
Phishing Simulator
Email Security Research Tool
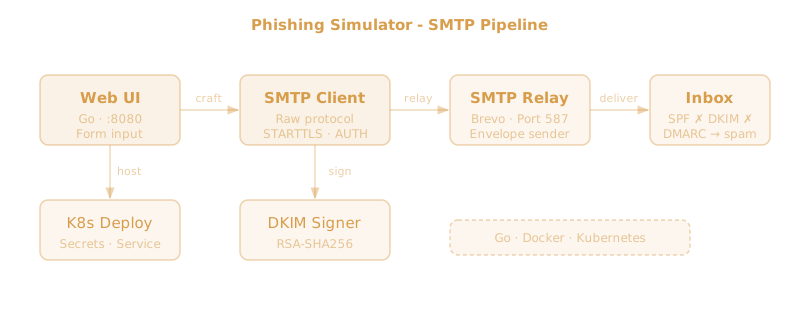
Phishing Simulator is an educational Go web app that shows why SPF, DKIM and DMARC exist. It sends test emails with a crafted sender header, so you can see how receiving servers flag them.
What he built
- SMTP built at the protocol level: a TCP connection on port 587, the EHLO handshake, a STARTTLS upgrade and AUTH PLAIN.
- Hand-written RFC 5322 headers that show the key point: the authenticated envelope sender and the displayed From header are independent.
- An explanation of each check that fails: SPF when the relay is not authorized for the domain, and DKIM when the domain's signature is missing.
- Deployment with Docker or Kubernetes, with secrets kept out of the code. It is for education only: sending spoofed email without consent is illegal.
Stack: Go, SMTP, Docker, Kubernetes
- Perl
- Python
- Go
- SMTP/DKIM
- Docker